
IoT Security Compliance Management
Simetric governs the SIM and eSIM layer where device identity, access, and audit trails actually live, so compliance holds up under scrutiny, not just on paper.

Powering Compliance-Ready IoT Operations for Global Enterprises
What Is IoT Security Compliance?
IoT security compliance is the set of controls, documentation, and practices enterprises use to prove their devices meet defined security standards. It also covers regulatory rules and internal risk policies. For organizations running IoT products across cellular, satellite, private network, and SIM or eSIM environments, compliance means more than device-level protection. It spans identity management, access control, firmware updates, and lifecycle records for every device in the fleet.
Traditional IT compliance assumes a fixed perimeter and predictable device behavior. IoT compliance can’t make either assumption. Devices sit outside the corporate network, connect through many carriers and connectivity models, and many run for years with little human oversight. That combination raises the bar for how enterprises track, govern, and prove their security posture at scale.
The stakes vary by industry, but the exposure looks similar everywhere. Utilities and oil and gas operators run IoT sensors across remote sites with no one watching. Connected fleets and logistics networks depend on devices that cross regions and carrier boundaries every day. Manufacturing and industrial sites connect sensitive data and critical systems that were never built for today’s cyber threats. In each case, one poorly secured device can open a door the enterprise can’t afford.
SIM-Level Security as a Compliance Control Point
Most conversations about IoT device security focus on hardware and firmware. But for cellular and satellite fleets, the SIM or eSIM is itself a key compliance control point, and it’s one that’s easy to overlook. It decides which network a device can reach and how it proves its identity. It also decides whether the device can be reset or shut off if compromised.
Enterprises running mixed SIM and eSIM environments need steady policy enforcement at this layer, not just at the device or application layer, and that holds true across carriers, regions, and device types. Preventing unauthorized access starts here: every SIM profile, credential, and network assignment should be set up, watched, and retired by policy, not tracked by hand across separate carrier portals.
This is where orchestration becomes a compliance function rather than a convenience. Enterprises need one layer governing SIM and eSIM lifecycle events, including remote provisioning aligned to standards like GSMA SGP.32. Without it, they lose the audit trail compliance frameworks require.
What NIST, ETSI, and IoTSF Actually Require
Enterprise IoT security compliance draws on several overlapping frameworks, each covering a different layer of the problem.
Together, they cover:
NIST SP 800-213 & NISTIR 8259
A federal baseline covering device identification, data protection, and access control.
ETSI EN 303 645
13 high-level rules now widely used as an enterprise procurement floor.
IoT Security Foundation Guidelines
A lifecycle-based framework covering governance, secure development, and operational resilience.
On their own, these frameworks describe good device design. At enterprise scale, they describe an operating discipline.
Related IoT & Edge Services
Connectivity Management Platform
Unified control across every carrier relationship.
Explore Connectivity ManagementSingle Pane of Glass (SPoG) Management
One unified view across devices and carriers.
Explore SPoG ManagementData Lake
Turn distributed telemetry into operational intelligence.
Explore the Data LakeWhy IoT Compliance Breaks Down at Enterprise Scale
Most enterprises know what secure IoT systems should look like. The problem shows up in execution: fleets can span tens of thousands of devices and dozens of carriers, and several internal teams often each own a different piece of the problem.
Gartner research on enterprise IoT risk found that most organizations have already deployed IoT at real scale, and a notable share have already faced an IoT-related attack in the past three years. Fewer than a third of CISOs felt confident they could assess and manage that risk. The gap isn’t awareness; most security teams already know the challenges they face. The real gap is a consistent way to apply security measures across a scattered environment.
Fragmented tools, inconsistent workflows, and siloed ownership across teams are what create the operational complexity that undermines compliance in practice. Enterprises rarely fail because they lack standards. They fail because no single system applies those standards consistently as devices move through onboarding, use, change, and retirement.
Zero Trust for Connected Devices
NIST SP 800-207 defines zero trust around a simple idea: no device, user, or network location is trusted by default. Every access request stands on its own, judged by identity, device health, and context, not by which network it came from.
Applied to IoT, zero trust means treating every connected device as its own resource. An industrial sensor and a fleet tracker each need their own check, every time, and enterprises can no longer assume trust just because a device sits inside a corporate network or a known carrier connection. For organizations running mixed fleets across public and private networks, this closes a real gap: device trust used to rest on network location alone.
This is exactly where the SIM-level control point covered above comes back in. Zero trust for connected devices has to be enforced at the credential layer, since that’s where a device actually proves its identity and where network access gets granted or revoked. IoT zero trust doesn’t replace existing device security controls. It coordinates them, applying the same checks and access rules to every device, no matter where it connects from or which network carries the link.
Where Enterprise IoT Compliance Fails
Even with the right standards on paper, enterprise IoT compliance tends to fail in a few predictable spots.
Poorly secured legacy devices often stay in service years past their intended life, with no one owning firmware updates or credential rotation for them. Supply chain gaps make it hard to confirm that IoT products from every manufacturer meet baseline security rules before deployment. And access control often breaks down across mixed environments, where devices cross multiple carriers, platforms, and admin boundaries, each with its own permissions model.
These gaps rarely come from weak security policy. They come from having no single system that tracks device status, connectivity, and lifecycle stage across the fleet. Without that view, compliance becomes a one-time audit instead of an ongoing state, a gap critical infrastructure and other critical systems operators can’t afford to carry.
How Simetric Supports Compliance-Ready Operations
Simetric doesn’t sell connectivity, SIMs, or security software. It acts as the enterprise orchestration layer that governs how connected devices move through their full lifecycle, coordinating that governance through more than 300 global carriers and 1,200+ normalized APIs. That’s what makes one authoritative record across carriers achievable in the first place, rather than just a promise on a slide.
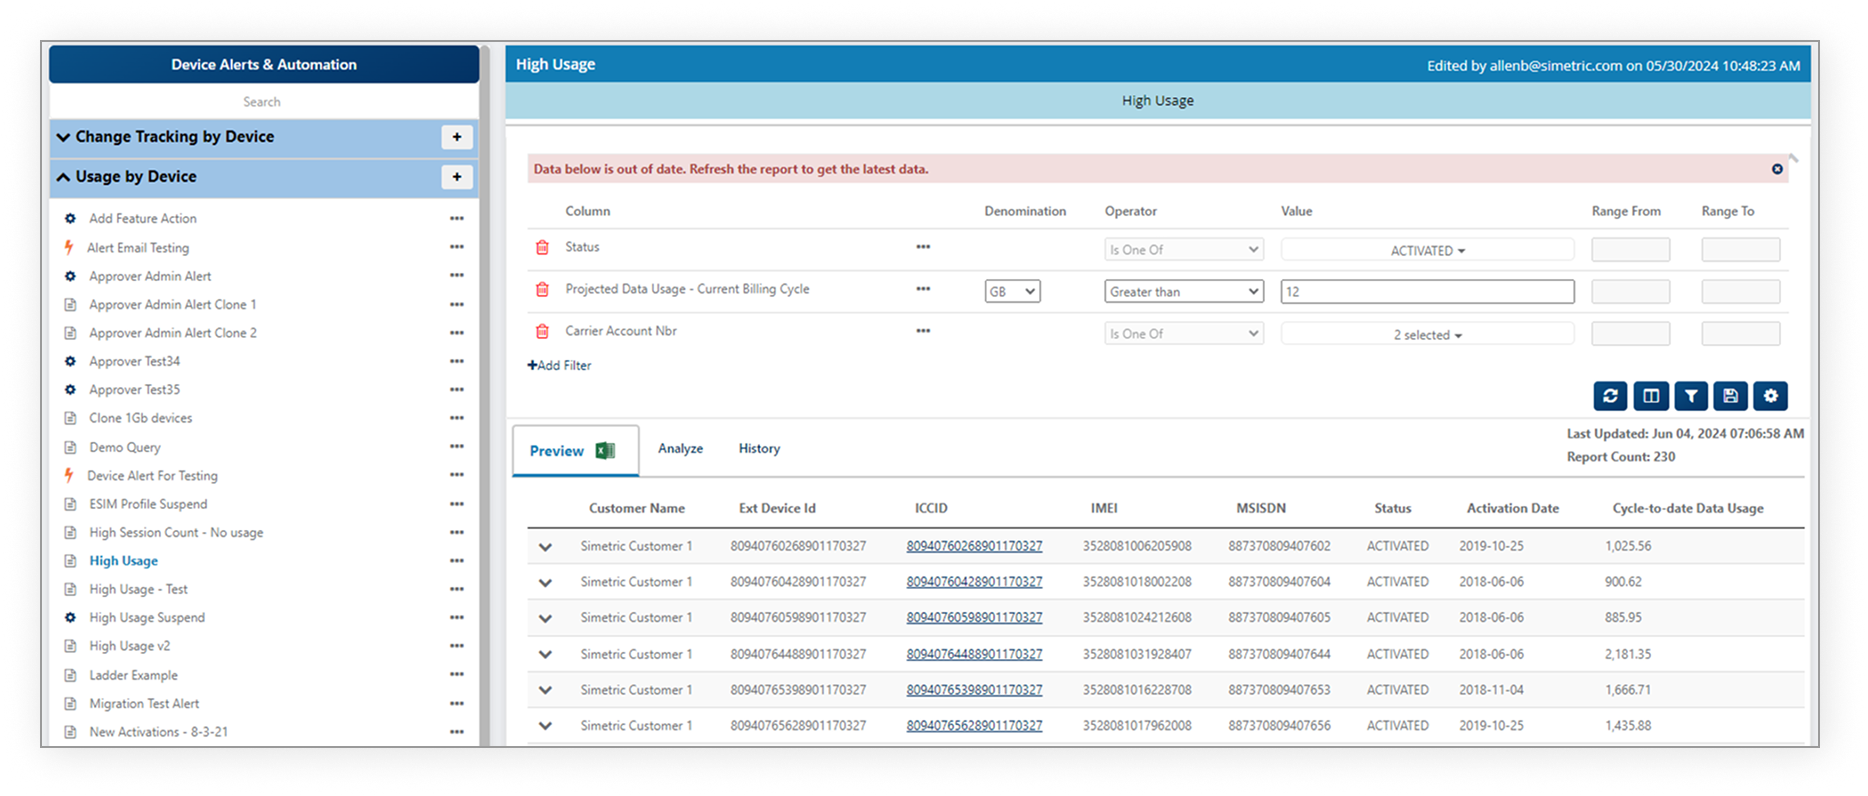
Across cellular, satellite, private network, and SIM or eSIM environments, Simetric coordinates lifecycle events, including onboarding, access and credential changes, firmware update tracking, and retirement. Enterprises can then show steady policy enforcement instead of piecing it together after the fact. Security and compliance teams get a single source of truth, not a patchwork of vendor dashboards.
This orchestration layer doesn’t replace the standards enterprises already follow. It makes sure those standards apply consistently, at scale, across environments that were never built to run under one policy. For enterprises managing mixed IoT fleets across critical systems, that consistency is what turns security frameworks into compliance they can actually show and prove.
Client Success in Action
Simetric gave us total visibility over 40,000 remote endpoint SIMs in 3 weeks.
VP of IT, Fortunte 500 Energy Utility
35% Reduction in Unused SIM Costs
90% Faster Anomaly Detection
A Closer Look at NIST, ETSI, and IoTSF
NIST SP 800-213 and the related NISTIR 8259 series define what federal agencies and enterprises should expect from IoT devices and their makers, setting a baseline covering device identification, data protection, and access control. Together, they give enterprises a shared way to judge whether an IoT product is secure enough to deploy.
ETSI EN 303 645 sets a security baseline built around 13 high-level rules. Though written for consumer devices, its baseline provisions, no default passwords, a clear way to report flaws, and regular software updates, are now widely used as an enterprise procurement floor, since they target the flaws behind most large-scale IoT attacks regardless of device category.
The IoT Security Foundation’s Best Practice Guidelines round out the picture with a lifecycle-based framework covering governance, secure development, device security, and operational resilience. Recent updates have lined up IoTSF’s framework with both ETSI EN 303 645 and NIST’s IoT guidance, giving enterprises one path for showing compliance across several standards instead of treating each one on its own.
On their own, these frameworks describe good device design. At enterprise scale, they describe an operating discipline: steady policy enforcement, recorded lifecycle events, and proof that holds up across every device and every connectivity model in use.
FAQs About IoT Security Compliance
What is IoT security compliance?
IoT security compliance is the ongoing practice of proving that connected devices meet defined security standards, regulatory rules, and internal risk policies. For enterprises, it covers device identity, access control, firmware updates, and lifecycle records across every device in the fleet, not just the devices themselves.
What standards apply to enterprise IoT security compliance?
The most cited frameworks are NIST SP 800-213 and the NISTIR 8259 series, ETSI EN 303 645, and the IoT Security Foundation’s Best Practice Guidelines. Recent versions of these frameworks are aligned with each other, so enterprises can work toward one consistent set of controls instead of separate checklists.
How does zero trust apply to IoT devices?
Zero trust for IoT means no device is trusted by default, even if it sits inside a corporate network or connects through a known carrier. Every access request is checked on its own, based on identity, device health, and context. NIST SP 800-207 defines the underlying principles.
Why is SIM-level security part of IoT compliance?
For cellular and satellite-connected devices, the SIM or eSIM controls which network a device can reach and whether it can be reset or shut off if compromised. Without consistent policy enforcement at this layer, enterprises lose the audit trail their compliance frameworks require.
Does Simetric provide IoT security software?
No. Simetric does not sell connectivity, SIMs, or security software. It acts as the enterprise orchestration layer that governs how connected devices move through their lifecycle, giving security and compliance teams the operational visibility and audit trail that compliance depends on.
How is Simetric different from a connectivity management platform (CMP)?
A CMP typically manages connectivity for a single carrier or provider. Simetric operates above carriers, connectivity platforms, and device types, coordinating lifecycle events across cellular, satellite, private network, and SIM or eSIM environments as a single operational system of record.